
Recently I wrote about how almost two million Air Canada customers were locked out of the Air Canada app following a security breach. Fortunately, only ~1% of those 1.7 million members (around 20,000) actually had their personal data compromised.
Well now British Airways has suffered a much bigger security breach, and I was one of those caught up in it.
I received the following email from British Airways:
From 22:58 BST 21 August 2018 until 21:45 BST 5 September 2018 inclusive, the personal and financial details of customers making or changing bookings at ba.com, and on our app were compromised. The stolen data did not include travel or passport information.
The breach has been resolved and our website is working normally.
We’re deeply sorry, but you may have been affected. We recommend that you contact your bank or credit card provider and follow their recommended advice.
We take the protection of your personal information very seriously. Please accept our deepest apologies for the worry and inconvenience that this criminal activity has caused.
UK media is reporting that 380,000 passengers have had their personal information compromised. This is almost twenty times as many people as with the Air Canada breach.
The following information has reportedly been stolen/compromised for customers who made bookings on BA.com or the BA app during the timeframe:
- email address
- postal address
- credit card number
- expiration date
- CVV
I’m not sure how widely the Air Canada breach was reported in Canada, but this British Airways data breach has been absolute headline news in the UK all weekend.
I would be surprised if Alex Cruz left the BA head office the entire weekend.
Early last week, I redeemed Avios for flights to Europe for next year. So that was within the timeframe identified by British Airways.
I used my British Airways American Express to pay for the taxes and fees for the flights, because I earn double Avios for spending with British Airways.
So I called American Express on Friday, and before I could even enter my card number, there was a hastily pre-recorded message regarding the British Airways breach, saying that they were aware of the problem, that card members would not be liable for any unauthorised transactions on their account, and that card members did not need to take any further action.
I also received the following email from American Express:
Dear Cardmember,
I’m writing to you about the reported British Airways data breach involving personal and financial details of customers being compromised through their web and mobile app.
We want to assure you we have industry-leading fraud protection technology that is continually monitoring for any suspicious activity in order to safeguard you. Also, our Cardmembers are never liable for any fraudulent charges on their Accounts. If you have used your American Express Card to book with British Airways, we are monitoring your Account for you.
There is no action you need to take – we will contact you immediately if there’s any unusual activity with your Account. In the meantime you can continue to use your Card as normal.
If we see any unusual activity which could be fraud, we will contact you immediately. For added protection, you can also sign up for free fraud and other Account activity notifications via email, SMS text messaging, or alerts through our app.
Thank you for your continued Card membership.
EU Data Protection Regulations
In May this year, strict new European Data Protection Regulations came into effect, commonly known as ‘GDPR.’ If you had provided your personal information to any companies operating within the European Union, you may have received various communications around this time advising you about how that company was complying with GDPR.
Here’s what I received from British Airways in May:
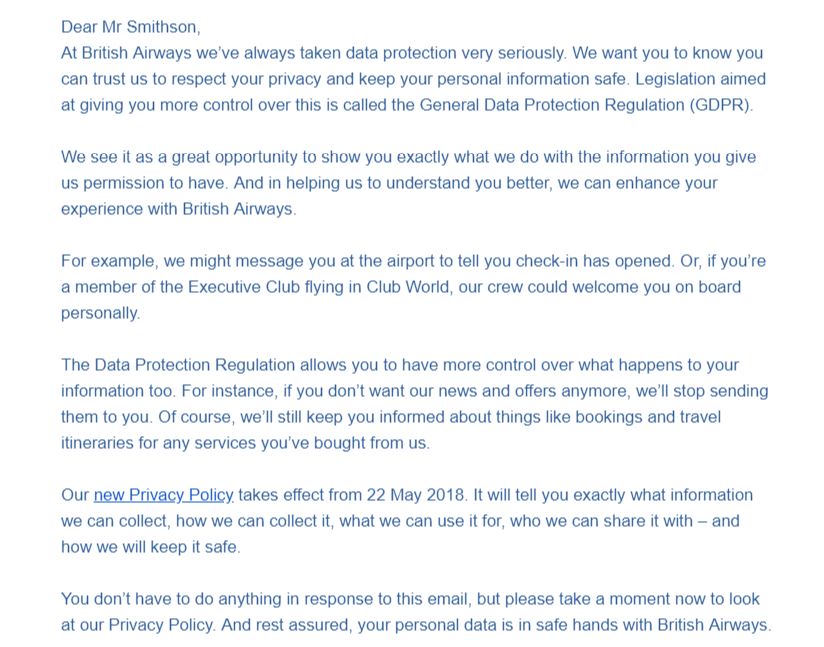
So GDPR is only a few months old, and there have been no breaches of the new regulations the size of the British Airways breach so far. Now breaches of GDPR rules can result in penalties of up to 4% of an offending company’s annual turnover (not profit).
British Airways breached GDPR by initially failing to properly notify customers within the required time frame of who they could contact if they had questions about the breach, and what steps British Airways would be taking to deal with the data breach.
So British Airways then (later) sent a second email to customers with this additional information.
The European Information Commissioner’s Office may choose to make an example out of British Airways as the first huge breach of GDPR by penalising them the full 4% of their annual turnover, which could be as much as £500 million, which is around ~$650 million.
IAG (British Airways’ parent company) shares dropped sharply on Friday following the news.
Bottom line
I must admit a chill went down my spine when I first heard the time frame of the breach, because I instantly knew I was within it.
I appreciate American Express reassuring me that I will not be suffering any financial loss as a result of the breach, but I’m wondering if I should be requesting a new card from American Express (i.e. with a new card number and security code) just to be on the safe side, even though American Express has advised that I do not need to do so.
If I do request a new card, in exactly one week’s time I’m going traveling for four months (which I’ll be sharing the details of with you over the coming days) so it’s highly likely the new card may not arrive in time before I leave. It will be my ’emergency’ card because I won’t be using it when paying in foreign currencies.
I’ll be very interested to see what action the Information Commissioner’s Office takes against British Airways as they could be facing a massive penalty. I’ll keep you updated as to what happens.
Of course I expect a few comments about ‘this is why I don’t fly British Airways,’ and I don’t profess to know enough about information security to understand if the data theft was due to negligence of British Airways’ part, or just bad luck. Remember Air Canada suffered a data security breach just a few weeks ago, and as cyber crime becomes more sophisticated we may see breaches like this more regularly.
If you have had your personal data compromised there is a special British Airways page with more information here.
If you were caught up in the British Airways breach what action are you taking? Are you requesting a new card?


Membership is free and takes no more information than commenting as a guest. Earn status points for good contributions, and see fewer ads as your status grows.