New: Check If You Were Impacted By The Marriott Data Breach

In late November 2018, Marriott revealed the details of a massive data breach. This involved Starwood’s guest reservations system, with an unauthorized party potentially copying and encrypting information all the way from 2014 until September 10, 2018.

How many people were impacted by Marriott data breach

At the time Marriott said that they believed this could contain information for up to 500 million guests, though in January they clarified that the information for “only” up to 383 million guests may have been compromised.
The compromised information included some combination of name, mailing address, phone number, email address, passport number, Starwood Preferred Guest account information, date of birth, gender, arrival and departure information, reservation date, and communication preferences.

On top of that, they specifically said that they thought approximately 5.25 million unencrypted passport numbers were included in the breach.

Marriott has done a pretty bad job handling the breach, in my opinion. A lot of people have requested that Marriott give members a way to figure out if they were impacted by the breach. Now, many weeks after the data breach was first revealed, they’ve done so.

You can now check if you were impacted by Marriott data breach

You can now request to find out if your personal information was compromised in the Marriott breach.
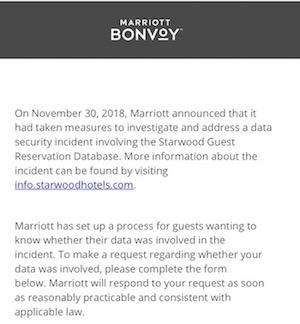
Note that:

  • This is being done by security firm OneTrust
  • You’ll need to share quite a bit of personal information to find out if you were involved (including the last six digits of your passport number); understandably, the last thing most people want to do after having their info compromised is sharing even more info
  • This isn’t instant; you have to submit your info, and then there’s a prompt saying “we will review your request and contact you shortly”
I decided to fill out the form about an hour ago, though haven’t heard back, so I’m not sure if “shortly” means a couple of hours, a couple of days, a couple of weeks, or what.

So you can use the checker at your own risk.

Will you be checking your Marriott breach “status?”

(Tip of the hat to TechCrunch)

Conversations (11)
The comments on this page have not been provided, reviewed, approved or otherwise endorsed by any advertiser, and it is not an advertiser's responsibility to ensure posts and/or questions are answered.
Comment as a member

Membership is free and takes no more information than commenting as a guest. Earn status points for good contributions, and see fewer ads as your status grows.

Type your response here.

If you'd like to participate in the discussion, please adhere to our commenting guidelines. Anyone can comment, and your email address will not be published. Register to save your unique username and earn special OMAAT reputation perks!

  1. Loading comments…
Recent Comments
The latest from the OMAAT community.

The comments on this page have not been provided, reviewed, approved or otherwise endorsed by any advertiser, and it is not an advertiser's responsibility to ensure posts and/or questions are answered.

Todd Diamond

What an absolute cluster. They publish a form that is right out of the "Phishing for Dummies" and "Phishing 101" handbooks. Here's the position everyone needs to take: Assume breach. Act accordingly.

0
‼ 0
Joe Guest

I'm guessing this company paid Marriott to do this service so that they can curate your data and sell it. There is zero reason why Marriott can't provide this service simply via your membership number. Providing all your personal info clearly is because this company has no access to your data but by you providing it you're giving them free info and who knows how accurate it even is.

0
‼ 0
mahjong Guest

Last 6 characters of Passport Number are optional but recommended. IMHO it is absurd to provide any information of a sensitive nature such as characters from a Passport Number after such a massive data breach.

0
‼ 0
Robert Hanson Diamond

They may have only announced this in Nov 18, but the breach was way before then, they just didn't tell us about it when it happened. I'd guess if you were "affected" by this, you would have seen the consequences by now on your own.

0
‼ 0
Andrew Diamond

Hard pass here, as well. Look: you've been compromised regardless. If you shopped anywhere online, it's just inevitable because we have near-zero legal protection for consumer identity. If HIPAA punishments applied to for-profit organizations, then you would see change. Until then, you're already compromised. Get in line for your free credit protection. (...or not. Thanks Marriott.)

0
‼ 0

Save posts to read later

Saving posts is a member feature. Become an OMAAT member to build a reading list you can come back to from any device.

Become a member
Meet Ben Schlappig, OMAAT Founder
5,883,136 Miles Traveled

43,914,800 Words Written

47,187 Posts Published