
Last week I wrote about how I discovered that my IHG account had been hacked and almost 80,000 points were stolen. The agent on the phone told me that my account would be disabled for three to five business days while they investigated the incident.
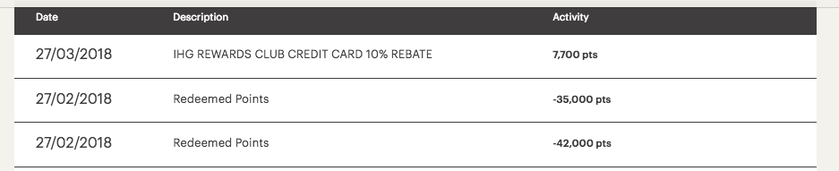
Sure enough, five days after that, they called me and told me that they restored the lost points in my account and were ready to reactivate it. They recommended that I change the e-mail address associated with the account, so I gave them a new one. I logged in and saw that my points were back.
Additional response from IHG
A couple hours later, I received an email from a person at IHG with the title “Executive Liaison.” It said:
Greetings from the Executive Office of IHG. The matter regarding the activity within your IHG Rewards Club Platinum Elite account has been forwarded to my attention for review.
I’m sorry that I wasn’t able to speak with you. I called your phone number but couldn’t reach you or leave a message. Programs such as IHG Rewards Club are occasionally the target of fraud. IHG takes the security of our members very seriously, and we implement active steps in order to maintain that security for our members and to prevent any loss. When a potential concern is brought to our attention, we take immediate action to protect both IHG and our members. Our standard protocol is for our internal Fraud department to complete an audit. While I understand your desire for additional information, we are unable to confirm any specific details of our investigations.
Moving forward, I do apologize for the delay in response from our Rewards Club center after your call about the activity in your account. I’m glad you were able to speak our Rewards Club office earlier today to change your email address and PIN, in addition to being advised of your points being returned and your account re-opened. Because of the frustration caused by the delayed response in gaining access to your account, I’ve deposited 15,000 points into your account. I know you would have preferred to have had access to your account and the points you’ve earned sooner, and for that I apologize. We do encourage you to ensure your IHG account is linked to a secure email address with 2 factor security authentication enabled, and that the security of your PIN is safeguarded.
If you want to discuss your concerns about this situation in more detail, please feel free to contact me at xxx-xxx-xxxx. I’m available Monday through Friday, 9 AM to 6 PM, Mountain Standard Time. In the event that I’m unavailable, please leave a message with your number and time when I can reach you.
Thank you for being an IHG Rewards Club Platinum Elite member. I hope we have the opportunity to host you as our guest soon.
Overall I was impressed with this response – 15,000 points was a nice show of good will, especially considering that I never complained to IHG about the length of time my account was frozen (it was less than a week, and that doesn’t seem unreasonable to me).
The ongoing concern
As many people pointed out in the comments of my previous post, the area where IHG really needs to improve is in account security. A few of the areas where IHG doesn’t seem to follow best practices are:
- A four-digit PIN serves as your password, and you can log in with just the PIN and your account number or the email associated with your account
- IHG doesn’t send an email to your previous e-mail address when the e-mail address associated with your account is updated
- When you reset your PIN, they email a new PIN to you, meaning that if you don’t change it, your IHG account is vulnerable if your email is hacked

Is it really cheaper for IHG to keep restoring points stolen from breached accounts than it would be for them to just invest in better account security? Haven’t high-profile breaches at companies like Target and Equifax taught organizations that data security is a worthwhile investment?
C’mon, IHG.
How can you protect yourself?
A few people in the comments on last week’s post mentioned AwardWallet, which notifies you when a redemption has been made on any of your linked accounts. That’s a good way to keep track of fraudulent activity across all your loyalty accounts.
You should also try to log into your accounts every month or so (had I done that, I would have caught this sooner), and change your PIN every now and then.
Do you have any other suggestions for how to safeguard your travel accounts from unauthorized access?


Membership is free and takes no more information than commenting as a guest. Earn status points for good contributions, and see fewer ads as your status grows.